How a Cybersecurity Resilience Centre Strengthens Enterprise Security
Organisations typically have an abundance of security data. The harder challenge is identifying which signals matter and responding quickly enough to stop an isolated incident from escalating into a major business disruption. This challenge is becoming increasingly complex as attack surfaces broaden across cloud infrastructure, applications, endpoints, identities, networks, and third-party services.
Attackers are also moving quickly. Verizon's 2026 Data Breach Investigations Report found that vulnerability exploitation had become the leading initial access vector, accounting for 31% of breaches analysed. The financial consequences remain significant, too, with IBM's 2026 Cost of a Data Breach Report putting the global average cost of a breach at USD 4.99 million.
Against that backdrop, security operations need to do more than generate alerts. Enterprises need the visibility, context and response capabilities to understand what is happening across their environment and act accordingly. A Cybersecurity Resilience Centre (CRSC) addresses this challenge by bringing monitoring, threat intelligence, detection, investigation and response into a more connected security operating model.
What Is a Cybersecurity Resilience Centre?
A Cybersecurity Resilience Centre is a coordinated security environment designed to help organisations continuously monitor their technology estate, identify potential threats, investigate security events, and respond to incidents.
A traditional Security Operations Centre (SOC) remains central to this model, but cyber resilience requires more than continuous monitoring. Security operations need context from threat intelligence, analytics to correlate activity across systems, response processes to contain incidents and wider controls that address vulnerabilities before they are exploited.
Intertec's Cybersecurity Resilience Centre brings these capabilities into a unified SOC architecture, incorporating technologies and frameworks including SIEM and SOAR, threat intelligence, User and Entity Behaviour Analytics (UEBA), Endpoint Detection and Response (EDR), MITRE ATT&CK, GRC systems, and security automation. The objective is not to collect more alerts, but to create enough visibility and context to determine which risks deserve attention and coordinate an effective response.
Why Fragmented Security Operations Create a Visibility Problem
A modern enterprise can generate security telemetry from dozens of sources. An endpoint platform may identify suspicious activity on a device while an identity system detects an unusual login. A cloud platform may generate another event, while a network control may record unexpected traffic. Individually, each signal can appear manageable. Viewed together, they may describe an attack in progress.
When security information remains fragmented across tools and teams, analysts must spend valuable time manually establishing those relationships. That can slow investigations and make prioritisation harder, especially when teams are already dealing with high alert volumes.
The external threat environment makes that fragmentation more consequential. Verizon's 2025 Data Breach Investigations Report found third-party involvement in 30% of breaches analysed, twice the previous year's level, and ransomware in 44% of breaches. The same report found that only 54% of perimeter-device vulnerabilities examined were fully remediated during the year.
Cyber resilience therefore depends on connecting signals across the environment rather than treating endpoint, network, cloud, identity and vulnerability data as separate security problems. Seeing relationships between events can help security teams move from isolated alerts to a clearer understanding of potential attack activity.
How 24/7 SOC Monitoring Creates Continuous Visibility
Continuous monitoring provides the operational foundation for a Cybersecurity Resilience Centre. Instead of relying on periodic security reviews or investigating only when users report suspicious activity, a SOC continuously observes security events across the technology environment. This can include infrastructure, networks, endpoints, applications, databases, cloud environments and other integrated sources.
Intertec's CRSC provides 24/7 monitoring, detection, analysis and response through its managed security operations. Its documented approach extends visibility across data, applications, networks, infrastructure, data centres, databases, cloud environments and third-party integrations.
Continuous visibility does not mean every alert requires human intervention. Its value comes from having enough telemetry and context to identify abnormal activity, investigate related events, and prioritise situations that require action. This is where correlation, analytics and automation become particularly important.
How AI and Automation Can Improve Threat Detection
Security teams have long used analytics and automation to process large volumes of telemetry. AI extends that capability by helping teams identify patterns, prioritise risks, and speed up investigation and response. The business case is increasingly measurable: IBM's 2026 Cost of a Data Breach research found that organisations making extensive use of AI and automation in security recorded approximately USD 1.93 million lower breach costs than organisations that did not use these capabilities.
That does not mean AI replaces security analysts. Its greater value lies in helping them work through large volumes of information more effectively. Within a connected SOC environment, analytics and automation can help correlate related security events, prioritise incidents, streamline investigation workflows, and orchestrate response actions. Human expertise remains important for interpreting context, investigating complex threats, and determining the appropriate response when business impact matters.
Intertec's CRSC architecture combines security telemetry with analytics, threat intelligence and security automation to support incident prioritisation, investigation and response. The operational objective is therefore not simply faster alert generation, but reducing the distance between signal, context and action.
Where Managed Detection and Response Fits
Continuous monitoring tells an organisation what is happening, but effective cyber resilience also requires the expertise and processes to determine what to do next. This is where Managed Detection and Response (MDR) complements SOC operations.
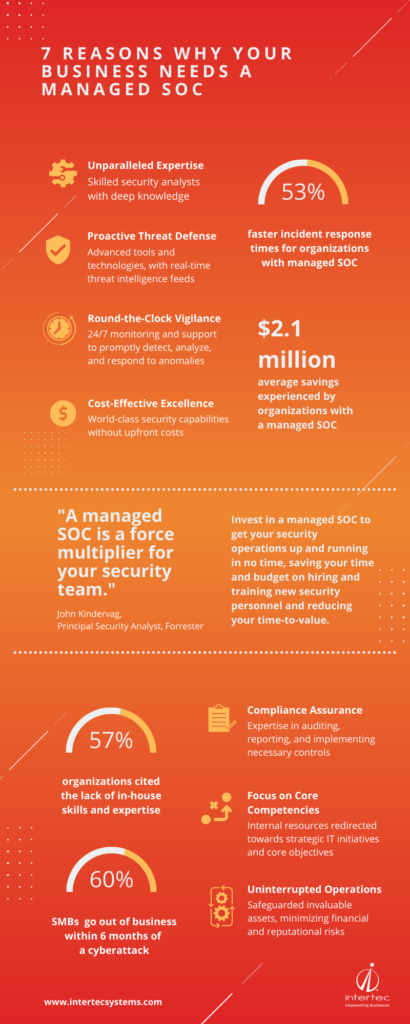
MDR combines ongoing monitoring with security expertise to investigate suspicious activity, prioritise incidents and coordinate response. It can be particularly relevant for organisations that need around-the-clock capabilities but don't want to build every specialist security function internally.
Intertec's SOC-backed MDR service provides continuous monitoring across cloud, network and endpoint environments, supported by threat analysis, human intelligence, security orchestration and automated response. Intertec also supports dedicated, shared and hybrid security delivery models, allowing organisations to align external security operations with their existing internal capabilities. Intertec Systems was recognised as a Major Player in the IDC MarketScape: Middle East Managed Detection and Response Vendor Assessment 2025.
For buyers evaluating MDR or a Cybersecurity Resilience Centre, the important consideration is not simply whether monitoring is available around the clock. They should also consider how incidents are prioritised, what investigation expertise is available, how response actions are coordinated and how the service integrates with the security investments already in place.
Why Threat Intelligence Needs to Be Connected to Operations
Security teams also need context beyond activity occurring inside their own environments. Threat intelligence provides information about emerging vulnerabilities, malicious infrastructure, attacker techniques, and active campaigns. Still, it has limited operational value when it exists only as a report that security teams must interpret on their own.
Its value increases when it informs day-to-day detection and investigation. Intelligence about an emerging attack technique, for example, can help analysts understand whether similar activity is appearing within the enterprise environment. Teams can incorporate indicators associated with an active campaign into monitoring and investigation workflows, while knowledge of attacker behaviours can help them assess seemingly unrelated events in context.
Within a Cybersecurity Resilience Centre, threat intelligence therefore becomes part of the detection and response cycle rather than a standalone information source. This connects awareness of the external threat landscape with what security teams observe inside the enterprise.
From Cybersecurity Operations to Cyber Resilience
A resilient organisation does not assume it can prevent every attack. It can maintain visibility, recognise suspicious activity, understand its significance, respond appropriately and strengthen its defences based on what it learns.
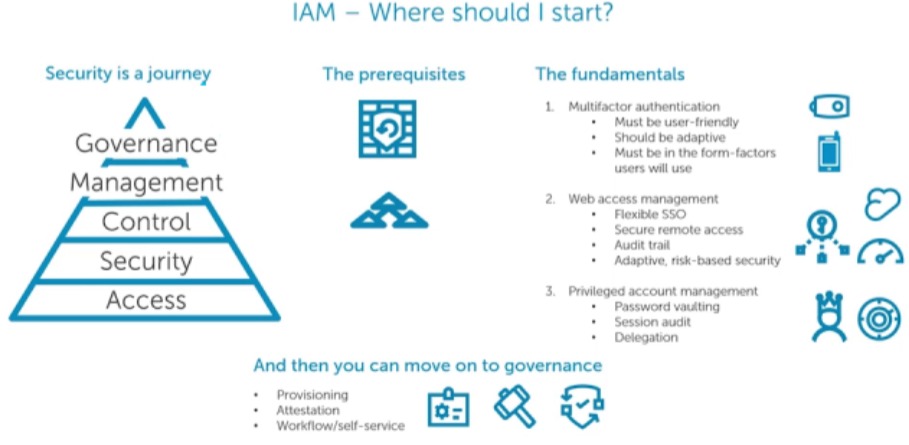
A Cybersecurity Resilience Centre supports that objective by connecting five operational capabilities:
- Visibility: Continuous monitoring across the enterprise environment.
- Context: Correlation and threat intelligence that help determine what security events mean.
- Detection: Analytics and security expertise that identify and prioritise potential threats.
- Response: MDR, orchestration and incident-response capabilities that enable action.
- Improvement: Vulnerability management, security testing and wider security controls that help reduce future exposure.
This is what differentiates resilience from monitoring alone. Monitoring can indicate that something has happened. A connected security operation goes further by helping teams understand the significance of that activity, establish the appropriate response and use what they learn to improve the organisation's wider security posture.
What Should Enterprises Look for in a Cybersecurity Resilience Centre?
Organisations evaluating a CRSC or managed security model should look beyond the number of technologies included in the service. A long tool list does not automatically produce stronger security outcomes. More useful evaluation criteria are operational: whether the service can provide visibility across the organisation's actual technology estate, correlate information from different security layers, incorporate relevant threat intelligence, and support investigation through to response.
Integration with existing investments is equally important. Organisations may already have SIEM, EDR, identity, cloud-security or vulnerability-management platforms in place. A resilience model should help those capabilities work together rather than automatically adding another isolated layer of technology.
The engagement model should also match the organisation's security maturity. Some enterprises may require a largely managed operation. In contrast, others need specialist capabilities that augment an established internal SOC. Ultimately, the right model closes gaps between detection, decision-making, and response while complementing the security capabilities the organisation already has.
Building a More Resilient Security Operation
As enterprise environments become more distributed, adding another standalone security product does not necessarily solve the underlying operational problem. The bigger challenge is connecting security information and expertise so teams can identify meaningful threats amid large volumes of activity and respond before those threats cause wider business disruption.
A Cybersecurity Resilience Centre provides a framework for doing that by bringing continuous SOC monitoring, threat intelligence, detection, MDR and incident response into a coordinated security operation. Intertec Systems' Cybersecurity Resilience Centre combines these capabilities within a unified SOC architecture designed to provide continuous visibility and support faster detection, investigation and response across complex enterprise environments.
For organisations assessing whether their current security operation can keep pace with a changing threat landscape, the starting point is understanding where visibility, detection and response remain disconnected and whether the existing operating model can turn security signals into coordinated action when it matters.
Explore Intertec Systems' Cybersecurity Resilience Centre to learn how a connected security operations model can strengthen enterprise cyber resilience.
https://www.intertecsystems.com/services/cyber-security
FAQs
Q. What is a Cybersecurity Resilience Centre?
A. A Cybersecurity Resilience Centre brings together security monitoring, threat detection, response and related cybersecurity capabilities. It provides a more coordinated approach to identifying and managing cyber risks across an enterprise.
Q. How is a Cybersecurity Resilience Centre different from a SOC?
A. A SOC focuses primarily on monitoring, detecting and responding to security events. A Cybersecurity Resilience Centre takes a broader approach by connecting SOC operations with capabilities such as application security, data security, GRC, Zero Trust and security testing.
Q. Why is 24/7 SOC monitoring important?
A. Cyber threats can occur at any time, so continuous monitoring gives security teams ongoing visibility into the security environment. It also helps organisations identify and investigate suspicious activity as it occurs.
Q. How does AI-driven threat correlation help security teams?
A. AI-driven threat correlation connects related security events and helps teams understand patterns across different sources of security data. This improves situational awareness and helps teams prioritise risks that need attention.